
Creating Applications
An application is a program that utilizes Apiture APIs. Applications can be created within the Developer Portal to receive secure keys that confirm your application has permission to access the APIs and any relevant data. Your application cannot access any of Apiture’s APIs or data without the secure keys.
Each application exist within an environment. Very similar applications, such as a development version of a Financial Institution’s (FI’s) website and a production version of an FI’s website, may exist; however, each of those websites would still be unique a application in the Developer Portal because they have different environments. For more information on managing and creating environment, see the environments article.
Applications also access a single FI. Each application has one environment and one FI. Even if the code base for several applications is very similar, every time there is a different FI or a different environment, a new application needs to be created within the Developer Portal.
Additional Profile Information
If you have not completed the information in your profile, a module will appear asking for your US Citizenship status and requesting you read the Terms and Conditions when you attempt to create an application. This information updates on your Profile once completed.
For more information on these questions, including notes on the U.S. Citizenship status question, see the Profile section.
Application Environments
All accounts can create an application in the shared Tiburon Community Financial (TCF) sandbox environment. Note: Real-world data should never be entered into the testing environment.
Dedicated environments are available once a company has been confirmed by Apiture. If you are expecting to see private environments and applications from your company but they are not displaying, ensure your account is connected to your company correctly and that your company has been validated by Apiture staff. See My Company in your Profile for more details.
From the Applications screen, click the Create Application button.
You will be asked what type of product you are using for the application. You may not have access to all types of products, as some products require an additional contract with Apiture.
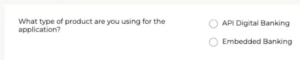
The choices are:
- API Digital Banking: Select this if you are accessing the APIs to manage Apiture Digital Banking
- Embedded Banking: Select this if you are creating an Embedded Banking Application
Once you select a product, a form opens below. The form is different for every product. Depending on the product type, the form may ask for the following information:
-
Application Name: A descriptive name of your application. This name is not visible by end users of your application. You may want to include a description of the environment(s) in the name if you have multiple, separated datasets used by a similar codebase, such as ‘Program (dev)’ and ‘Program (prod).’
-
Application Type: Choose from four standard types,: Regular web application, Single page web application (SPA), Native application (desktop or mobile), or Machine-to-machine (M2M) application. This determines the authentication method and which fields appear on the form.
-
Authentication: Automatically derived from the Application Type you select, this field is read-only and cannot be set independently.
-
Regular web application, SPA, or Native application: Displays “Authorization Code Grant Flow (with PKCE).” PKCE is always required; there is no longer an option to use Authorization Code Flow without it. A Redirect URL is required for these types.
-
Machine-to-machine (M2M) application: Displays “Client credentials.” No Redirect URL, no PKCE, and no refresh token are involved; M2M clients authenticate directly with their client credentials.
-
Site URL / Download Location: A URL of a web page with additional information about the application, including information on downloading or licensing the application.
-
Redirect URL: Only required for Authorization Code Flow. The authorization server will redirect to this URL to complete the OAuth authentication process. This is required for the Authorization Code Flow authentication option. You can add up to 8 redirect URLs.
-
Description: A markdown description of the application. Apiture recommends including the FI and the environment in the description for easy visibility. The markdown formatting can be checked by clicking the preview button above of the textbox.
-
Products [and APIs]: Select the various Apiture products the application will use. Each API product comes with at least one API that the product uses. The All Embedded Banking Components product come with all of the currently available Embedded Banking components and any related APIs. If applicable, also select the specific APIs your application uses and deselect the APIs that are not needed for your application. For security purposes, please only select products that the application is using.
-
- Environments: Select the environment or multiple environments the application can access. Read this article for more information on environments.
-
Maximum Connection Hours: For non-production environments of certain products, such as Embedded Banking Components, the maximum connection hours can be customized. The user will be logged out automatically after this time. This can be lengthened or shortened to make development easier. These connection hours are not used in production environments for security purposes.
- Excluded Scopes: Scopes are what an application or API is allowed to do. The list of scopes is completed automatically based on the products selected. Usually, the automated scope selection are appropriate for an application. For more information on scopes, read this article.
The scopes for an application may rarely need to be modified. For example, if an is only displaying information, but not creating new information, it should be limited to read-only scopes. Check the Exclude Write Scopes option if your application does not need to create or edit any data to quickly exclude all scopes that allow writing data. Other scope customization can be done by clicking the checkmark next to specific scopes that your application does not require.
Note: Application Type cannot be changed after an application is created, since it fixes the authentication method and security requirements. If you need a different type, create a new application.
Once this information has been completed and the application requires manual approval from Apiture. Once Apiture approves or denies an application, the user who created the application will receive an email with information on next steps.
How can we help?
Get support for your issues.